


Distributed Industrial Infrastructure
Making Complexity Manageable
Decentralized structures enable flexible production, but they also increase the digital attack surface. Centralized management across all locations allows for the secure administration of machines, devices, and remote access, helping to keep growing complexity under control. This article explains what is important for centralized management and how it can be implemented using the Endian Secure Digital Platform.
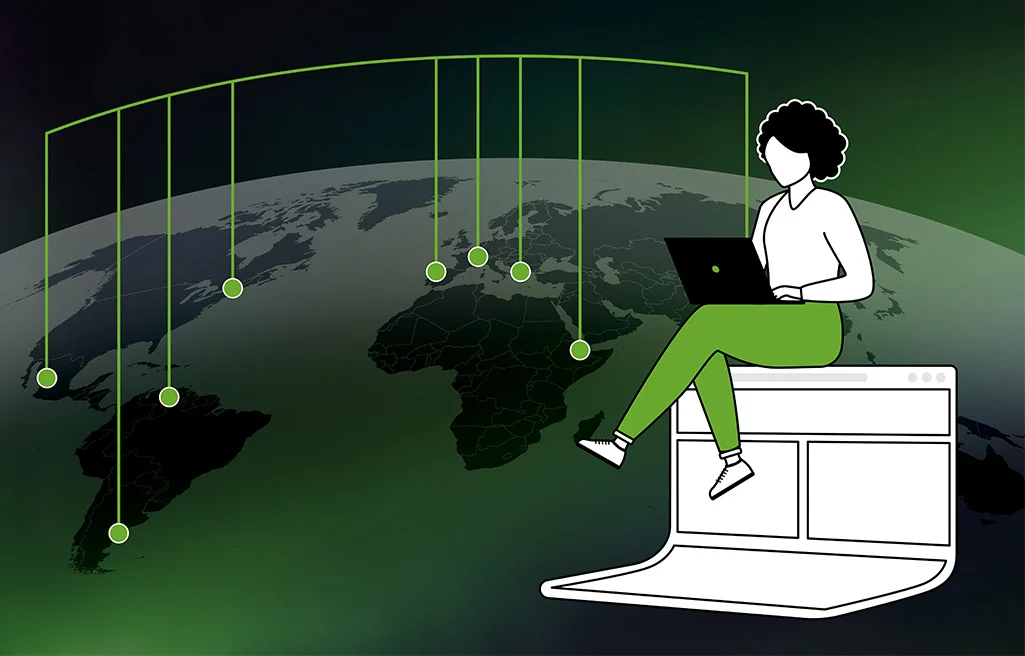
“Products are no longer created in isolated value chains, but rather in complex networks of suppliers, platforms, services, and digital infrastructures,” says the Federation of German Industries (BDI), describing the reality of today’s manufacturing landscape. For many companies, machines and equipment are located at globally distributed production sites, regional branches, or directly at the customer’s premises.
The concept of Industry 4.0 has led to these distributed systems being closely interconnected digitally: machines and IT systems can automatically exchange data, and service technicians have the ability to access distant systems from anywhere in the world via remote access. This extensive interconnectivity increases the efficiency of manufacturing companies, but at the same time it expands their digital attack surface. It is no longer enough to simply secure machines and facilities; all digital components that enable communication between them must also be secured.
Complexity as a Security Risk
The sheer number of devices and connections has greatly increased the complexity of industrial network environments, and in environments that have evolved over time, it is not always clear which components and connections actually belong to the infrastructure: Over the years, outdated components have been replaced with more modern ones, or service providers have set up remote access to perform maintenance work. If comprehensive documentation is also lacking, potentially dangerous security vulnerabilities can arise. After all, those responsible can only secure what they are aware of.
Furthermore, different security standards may apply at the various distributed locations. This can significantly increase the cyber risk if attackers penetrate the networks through a vulnerability and then spread laterally. Finally, the use of different tools and security systems complicates the deployment of uniform security updates, leaving parts of the production environment unprotected and providing attackers with a potential point of entry.
Creating Transparency, Segmenting Networks
Bringing increasing complexity under control is one of the greatest challenges for companies with decentralized structures.
To do this, decision-makers first need an overview of which devices can establish a digital connection. Network visualization—the graphical representation of structures, relationships, and data flows—makes it possible to clarify the connections within the company as well as beyond the network’s boundaries. Administrators can see which systems are in place, who is authorized to access them, and how they typically communicate with one another.
Together with an assessment of the security requirements for the various systems, these visualized network structures provide the basis for network segmentation. To achieve this, a single, interconnected network is divided into several small subnets, which increases the level of protection: In the event of a cyberattack, the ability of the attack to spread within a network often determines the extent of the damage. With consistent network segmentation, the attack remains confined to a local area. In a flat network, on the other hand, there would be nothing to stop it.
Endian 4i Security Gateways
Network segmentation can be implemented using Endian 4i Security Gateways. These gateways are equipped with several coordinated security features. The Intrusion Detection and Prevention System (IDS/IPS) scans incoming data streams for potential malware and blocks dangerous programs. A firewall prevents unauthorized connections. All data transfers are encrypted via a Virtual Private Network (VPN), ensuring that the data cannot be intercepted or tampered with.
In addition, the Endian 4i Security Gateways have their own computing capabilities, allowing them, for example, to perform data analysis at the network edge. Docker is preinstalled, making it easy to deploy analysis programs via containers. As a result, the Endian 4i Security Gateways not only ensure security but also help reduce the number of connections to external servers and platforms.
Centralized Management for Decentralized Structures
Once all devices and network segments have been identified and secured, their centralized management is the next crucial step in bringing complexity under control. Centralized management helps enforce consistent security policies so that all decentralized branches maintain the same level of protection. At the same time, it enables the centralized deployment of security updates to close vulnerabilities consistently and as quickly as possible.
The Endian Secure Digital Platform consolidates monitoring, configuration, and control of all devices into a single interface, automates key tasks, and thereby reduces the workload on administrators. Security software updates are rolled out automatically, ensuring that all devices are up to date at all times. In addition, the platform monitors configurations, certificates, and system statuses so that deviations from defined policies can be detected early on.
Standardizing Remote Access
Centralized management of all remote access is another key component for greater security and reduced complexity, because decentralized and disorganized access rights management creates an enormous administrative burden and almost always leads to dangerous security vulnerabilities.
With Endian Switchboard, the management tool of the Endian Secure Digital Platform, all access can be managed centrally. Following the “least privilege” principle, administrators can define roles and assign individual permissions to users or user groups. This ensures that each user has access only to devices relevant to their tasks.
For the login process, Endian relies on Zero Trust Network Access (ZTNA). With this approach, every request and every session is approved individually, whereas traditional remote access trusts the user as soon as they log in.
For even greater transparency, access can be logged.
Conclusion
Distributed production environments do not necessarily have to lead to unmanageable security structures. What matters most is that companies can centrally monitor all locations, devices, and connections and consistently enforce security policies. The Endian Secure Digital Platform combines network monitoring, configuration, access control, and updates into a single, centralized interface. Automated processes further simplify management and reduce the workload for administrators. Even complex, decentralized production networks can be easily and securely managed through this platform.
Frequently Asked Questions
Why do decentralized corporate structures pose a potential risk to IT security?
In decentralized companies, machines and IT systems exchange data. Due to the large number of devices and systems involved in this process, it is not easy to identify what needs to be secured. This can lead to dangerous vulnerabilities. Differing security standards further increase the risk.
How does network segmentation limit the consequences of a cyberattack?
Segmentation divides a connected network into several small subnets. This requires network visualization and an assessment of the security needs of individual systems. If attackers manage to gain access, the attack remains localized thanks to the segmentation. In a flat network, however, they can spread laterally.
What security features do the Endian 4i Security Gateways offer?
The Endian 4i Security Gateways combine an Intrusion Detection and Prevention System (IDS/IPS), a firewall, and VPN encryption for every data transfer. They also feature their own computing capacity and come with Docker pre-installed. This allows data to be analyzed right at the network edge, resulting in fewer connections to external servers.
How does the Endian Secure Digital Platform centrally manage decentralized locations?
The Endian Secure Digital Platform consolidates monitoring, configuration, and control of all devices into a single interface. It automatically deploys security updates and checks configurations, certificates, and system statuses. Administrators can detect deviations from defined policies early on and maintain the same level of protection across all branches.
How can remote access to industrial systems be uniformly secured with Endian?
The Endian Switchboard centrally manages all remote access. Administrators define roles based on the least-privilege principle, ensuring that users can only access devices relevant to their tasks. Zero Trust Network Access (ZTNA) authorizes each request and session individually. Additionally, access can be logged.